Windows Update certificates expire in May and June 2027. Microsoft is rotating the certificates used to establish trusted connections to its Windows Update service. Devices without the replacement certificates may lose direct access to Windows Update after the applicable deadline. For most supported and regularly patched Windows devices, no additional action is required.
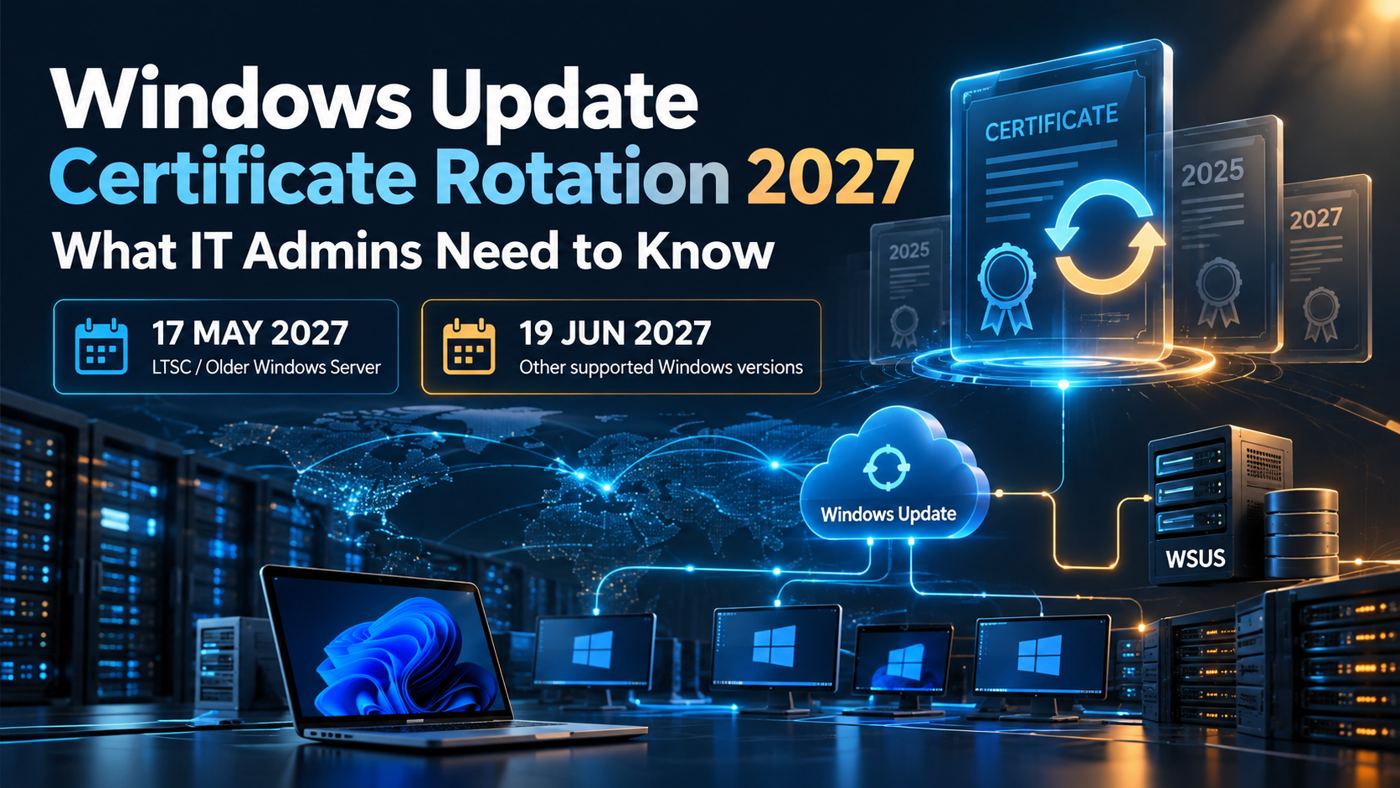
Windows Update certificate rotation 2027: deadlines
The two certificate expiration dates are May 17, 2027 and June 19, 2027. The necessary security update depends on the Windows release.
| Windows release | Required action | Deadline |
|---|---|---|
| Windows 11 25H2 and later | No additional action | None |
| Windows 11 24H2 and Windows Server 2025 | September 2025 security update or later | June 19, 2027 |
| Other supported Windows 11 releases and Windows Server 2022 | July 2026 security update or later | June 19, 2027 |
| Supported Windows 10 releases | July 2026 security update or later | June 19, 2027 |
| Windows 10 Enterprise LTSC 2019, Windows Server 2019 and Server 2016 | July 2026 security update or later | May 17, 2027 |
| Unsupported Windows releases | Upgrade to a supported version | Before access is lost |
Does this affect SCCM, WSUS or Intune?
WSUS / Configuration Manager (SCCM): Microsoft explicitly states that this certificate rotation does not apply to devices receiving updates from Windows Server Update Services (WSUS). In SCCM environments using a WSUS-backed Software Update Point, distinguish those clients from devices that scan Microsoft’s cloud Windows Update service directly. The exemption is based on the device’s update source, not simply whether SCCM is installed.
Intune / Windows Update for Business: Devices using cloud Windows Update should remain current with monthly security updates. Use Intune reporting, update policies and device inventory to identify older, offline or outdated machines that may require remediation.
What should IT administrators do now?
- Identify affected releases: Inventory supported, outdated and unsupported Windows versions across clients and servers.
- Review patch compliance: Verify the relevant September 2025 or July 2026 security update baseline, or any later cumulative update, is installed.
- Confirm the update source: Separate direct Windows Update devices from WSUS-managed devices, especially in co-managed environments.
- Remediate gaps: Update supported devices and plan replacement or upgrades for unsupported operating systems.
If a supported device misses its deadline, administrators can obtain the required cumulative update from the Microsoft Update Catalog and distribute it using their regular management tools. Windows Update access may otherwise be unavailable until remediation is completed.
Key takeaway
This is not the Secure Boot certificate rotation. It concerns certificate-based trust for Windows Update connectivity. Keep supported Windows devices patched, verify older systems and prioritize the May 17, 2027 deadline for Windows Server 2016/2019 and Windows 10 Enterprise LTSC 2019.
Official reference: Microsoft: Prepare for Windows Update certificate rotation in 2027 (October 8, 2026).
Leave a Reply